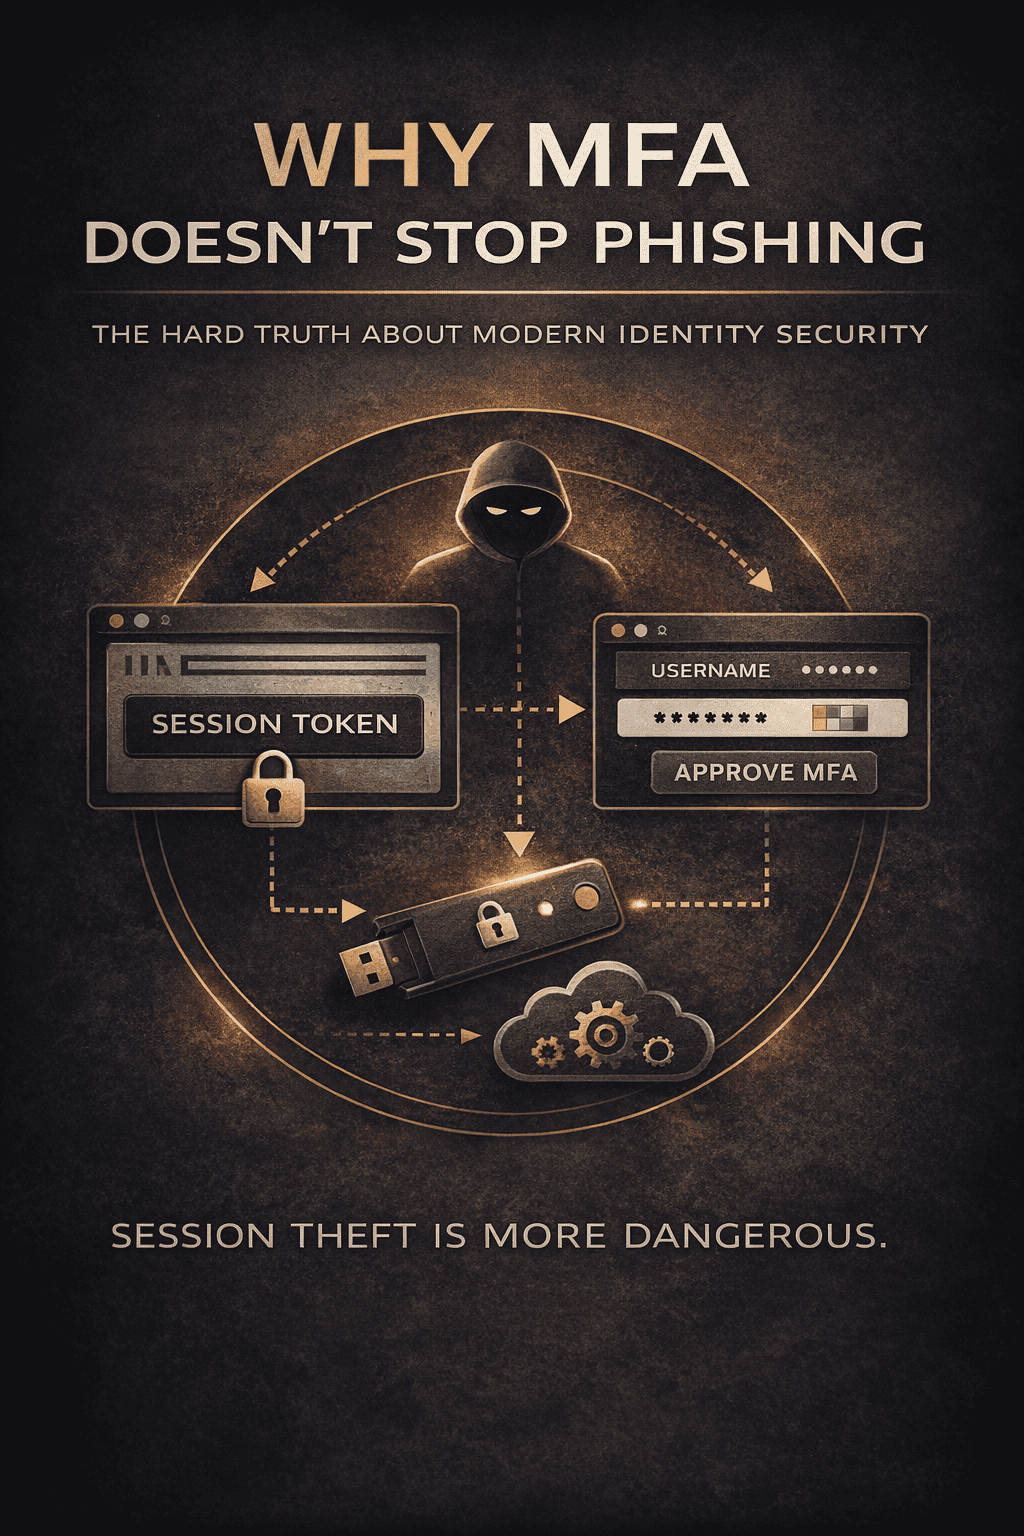
Why MFA doesn’t stop phishing becomes clear when you understand how attackers target sessions instead of passwords.
Why the MFA distinction matters
Why MFA doesn’t stop phishing is one of the most misunderstood problems in modern cybersecurity.
Most security teams still operate under an outdated assumption:
password + MFA = secure account
That model no longer matches how modern identity attacks work.
MFA still helps against credential stuffing, password reuse, and many basic account-takeover attempts. But MFA is not one security property. Codes and approval prompts can be relayed or socially engineered, while phishing-resistant cryptographic authentication is designed to bind the ceremony to the legitimate service.
The result is simple but uncomfortable:
Conventional MFA often protects the login challenge, not every authenticated state that follows it.
That distinction matters because the real asset in modern cloud environments is no longer just the password. It is the authenticated session: a cookie, token, or trusted state that can persist after the prompt is gone.
If your security model stops at “MFA enabled,” you are defending the wrong layer.
This is exactly why MFA doesn’t stop phishing in many real-world attacks.
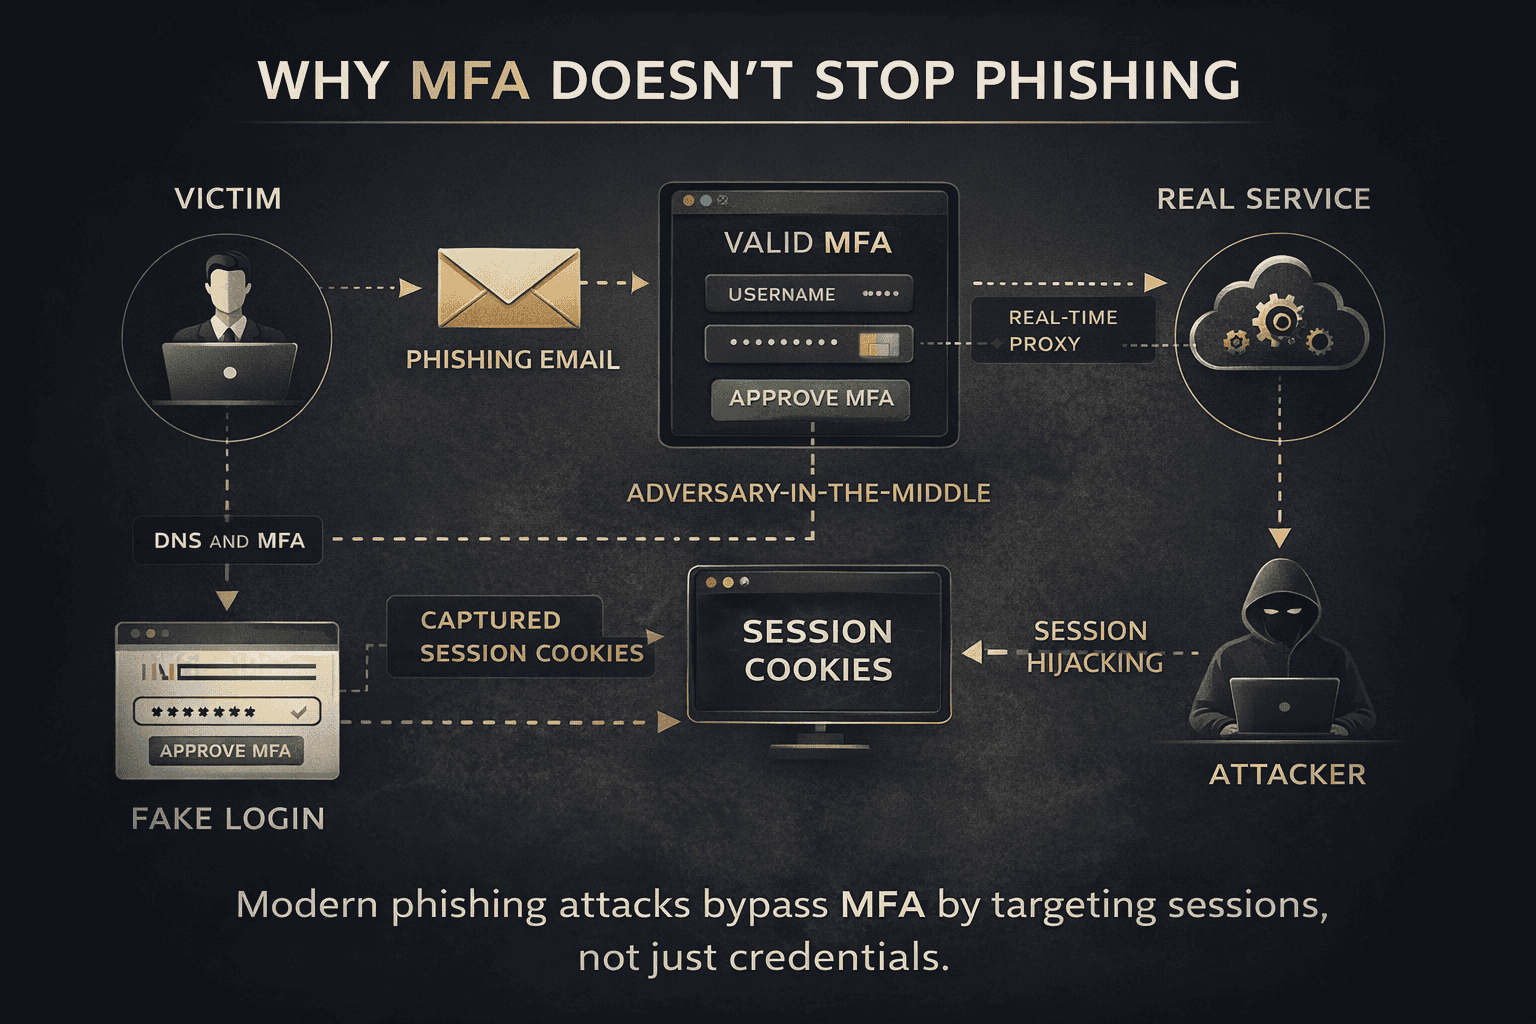
The diagram illustrates how a phishing flow can target session state instead of only a password.
The Core Mistake: Treating Identity as a Login Event
Many organizations still think of authentication as a single event: a user enters credentials, completes a second factor, and gets access.
That is no longer how identity works in practice.
Modern identity is a chain:
authentication → token issuance → session establishment → reuse → refresh → policy reevaluation
An authentication method protects one point in that sequence. The remaining risk depends on session design, context evaluation, device trust, recovery paths, and the platform’s response to risk.
This is the core strategic mistake in modern identity security:
teams protect the login, but attackers target the trusted state created by the login.
Why MFA Solved Yesterday’s Problem
Multi-factor authentication is an important improvement over password-only sign-in, but its protection depends on the method and the surrounding system.
The old problem looked like this:
- attacker steals a password
- attacker attempts login
- second factor blocks access
- attack fails
Against that model, MFA remains a strong improvement over password-only security.
But identity systems evolved. Cloud services, SaaS platforms, federated sign-in, OAuth, OpenID Connect, SAML, session cookies, access tokens, and refresh tokens changed the attack surface.
The attacker’s goal shifted from:
“Can I steal the secret?”
to:
“Can I obtain or replay a valid identity state?”
That can be a serious problem because a valid session artifact may let an attacker operate within the user’s context until policy, binding, expiry, or revocation stops it.
Where MFA Actually Breaks
Authentication is not the same as session trust
Conventional MFA protects an authentication challenge.
It does not automatically protect every artifact the system issues after the challenge succeeds.
Once a service grants:
- session cookies
- access tokens
- refresh tokens
the security question changes. If an artifact can be stolen, replayed, or reused from another context, a service may continue to treat the holder as legitimate until another control intervenes.
That is why many identity breaches today are not about defeating MFA directly. They are about abusing what happens after MFA succeeds.
Session artifacts need their own protection
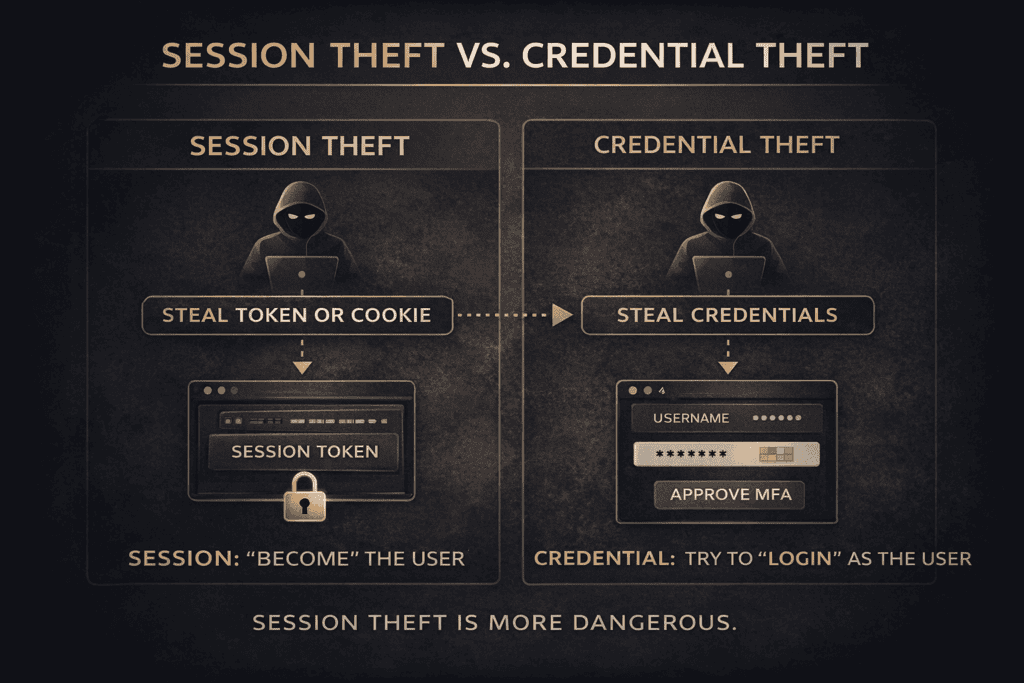
The diagram below shows the difference between session theft and credential theft in modern identity attacks.
In Microsoft 365, Google Workspace, Slack, Salesforce, and similar platforms, access is often governed by tokens and sessions rather than by the password itself.
That means:
a stolen bearer artifact may be reusable as the user until the relevant controls reject or revoke it
Session theft is different from credential theft. The attacker is attempting to use an already trusted state rather than prove control of the original authenticator. Its impact depends on token type, binding, policy, expiry, and detection.
Trust can persist longer than the risk decision
Many organizations still allow sessions to remain valid too long, refresh silently, or avoid meaningful re-evaluation unless the token naturally expires.
That creates operational space for attackers.
An account owner may change the password, suspect something is wrong, or even sign out in one location, while a stolen session remains usable elsewhere. If risk-based reevaluation is weak, the attacker keeps the benefit of the earlier trust decision.
The user remains inside the security boundary
Push approvals, codes, and interactive login prompts all assume the user can reliably make safe decisions in real time.
In reality, users are:
- busy
- conditioned by repetitive prompts
- overloaded by email and app notifications
- operating on mobile devices
- trained to move quickly
Modern phishing exploits exactly that environment.
Attackers do not always need to beat the user. Sometimes they only need the user to cooperate at the wrong moment.
Weak fallback paths undermine strong primary controls
A company may deploy security keys or passkeys and still leave open:
- SMS fallback
- insecure recovery email flows
- helpdesk override procedures
- legacy authentication protocols
- unmanaged device exceptions
At that point, the environment is not protected by its strongest control. It is exposed through its weakest allowed route.
The Real Attack Paths That Bypass Traditional MFA
Adversary-in-the-Middle (AiTM) phishing
AiTM phishing uses an intermediary phishing service to present a convincing sign-in experience while relaying the victim’s interaction to a legitimate service.
When a user enters a password, an OTP, or approves a push in that flow, an intermediary can relay the interaction. Depending on the application and session controls, it may obtain artifacts that can be replayed. This is why code entry and approval alone are not phishing-resistant.
This is the hard truth many teams still resist:
A conventional MFA challenge can succeed while the wider identity system is still exposed.
The problem is not always failed authentication. It can be a successful authentication that is relayed, followed by misuse of a session artifact.
This is the core reason why MFA doesn’t stop phishing when attackers use AiTM techniques.
Session hijacking
In some attacks, the phishing page is not even the main issue.
If an attacker obtains a valid session cookie or token, they may be able to operate in the user’s session context without presenting the original password again. Whether replay succeeds depends on the artifact, application, token binding, policy, and expiry.
This is post-authentication compromise, and it is exactly why login-centric defenses are no longer enough.
Push fatigue and approval abuse
Not all MFA bypasses are technically advanced.
For example, attackers may create repeated prompts and pressure a user to approve one. The weakness is workflow manipulation, not a failure of cryptography.
OAuth consent phishing is a separate permission path
Some attacks do not try to steal credentials at all.
Instead, the victim is tricked into authorizing a malicious or overprivileged application. A granted consent can give that application delegated access to data or APIs within the scope and lifetime of the permissions and tokens involved.
This is not the same as stealing a browser session. Response should include reviewing the application, requested permissions, consent grant, associated tokens, activity, and affected data. A password reset or MFA prompt alone does not remove an illicit consent grant.
Legacy authentication and weak recovery
Older protocols, weak password reset processes, unmanaged devices, and insecure exception handling remain common attack paths.
Security teams often celebrate strong frontline controls while leaving side entrances open.
Attackers notice that immediately.
The Real Shift: From Credentials to Identity State
The old mental model was simple:
steal password → gain access
The new model is more accurate:
obtain valid identity state → operate as the user
That identity state may include:
- an authenticated session
- valid access or refresh tokens
- a trusted device context
- an approved OAuth application
- a low-risk sign-in posture in the identity provider
This is why identity defense now has to move beyond passwords and beyond the login screen.
The real perimeter is no longer static authentication.
It is dynamic session integrity.
Why Traditional Security Awareness Falls Short
Most awareness programs still teach users to:
- avoid suspicious links
- check for spelling mistakes
- look at the sender address
That is not enough against modern phishing.
Today’s attacks are often:
- visually convincing
- contextually relevant
- timed to business processes
- proxied through realistic login flows
- designed to exploit approval habits, not obvious mistakes
The skill users actually need is more advanced:
they must know when not to approve identity-related actions, even when the flow feels familiar.
Security awareness has to evolve from “spot the typo” to recognizing abnormal identity workflows under pressure.
Why MFA Feels Safer Than It Sometimes Is
There is a dangerous psychological effect here.
When a user sees:
- a familiar Microsoft or Google login flow
- a real MFA prompt
- a successful sign-in
they often interpret that as proof of legitimacy.
But in an AiTM attack, the attacker is relaying that exact flow in real time.
That means a familiar conventional MFA flow can become, in the user’s mind, a false signal of trust rather than proof that the origin is legitimate.
This does not mean MFA is useless.
It means OTP and approval-based MFA are often not origin-bound.
It verifies that a factor was completed, but a manually entered code or approval does not by itself cryptographically bind the result to the intended relying party.
What Actually Works
Use phishing-resistant authentication
The strongest structural improvement is to offer and, where risk warrants, require phishing-resistant cryptographic authentication such as:
- FIDO2 security keys
- passkeys
- device-bound cryptographic authenticators
FIDO2 and WebAuthn use public-key cryptography and relying-party or origin binding. A credential registered for the legitimate service cannot normally produce a valid assertion for a lookalike origin.
That sharply reduces the value of proxy-based credential phishing because an attacker cannot simply relay a valid assertion to another origin. It does not eliminate malware, compromised endpoints, recovery abuse, malicious authorized applications, or every form of post-authentication compromise.
This is not just “better MFA.”
It is a different security property, not an absolute account-takeover guarantee.
Passkeys may be synced across a user’s devices or bound to one device or security key. Both models use phishing-resistant cryptographic authentication, but they make different recovery, portability, and synchronization-fabric assumptions. Select the model that fits the service and assurance requirement.
Enforce device and context trust
Authentication without context is weak.
A stronger model asks:
- is this a compliant device?
- is the browser trusted?
- does the location make sense?
- is the sign-in risky?
- is the user’s behavior consistent?
- should this session exist under these conditions?
This is where Conditional Access, device compliance, managed browsers, and risk-based policies become critical.
Reevaluate trust continuously
A session should not remain trusted simply because it was once established successfully.
Continuous reevaluation matters because risk changes over time.
A user account may become high risk. A token may appear in a suspicious context. A session may suddenly behave differently from its baseline.
If reevaluation is slow, attackers keep access longer than they should.
When reevaluation is fast and supported by the application, it can shorten the time a compromised session remains useful.
Treat tokens as high-value secrets
Many teams still protect passwords more seriously than tokens.
That leaves a material gap.
In modern cloud identity, tokens can authorize systems, data, and workflows. They should be protected, bounded, monitored, and revoked or invalidated according to the platform’s supported controls when risk changes.
Detect abuse after authentication
A major failure in many programs is that visibility drops after login succeeds.
That is the wrong point to stop watching.
Teams need detection for:
- unusual session reuse
- mailbox rule manipulation
- abnormal API behavior
- suspicious OAuth consent activity
- unusual access patterns after sign-in
- token reuse from unexpected contexts
The breach often becomes visible only after authentication is complete.
Eliminate weak fallbacks
Strong identity systems are undermined by weak recovery and legacy exceptions.
If you allow phishable fallback methods, attackers will route around your best control.
This is why many identity hardening projects fail. The organization deploys something strong, then preserves enough weak exceptions to keep the overall environment exposed.
Build real identity incident response
A password reset alone may not be enough for a modern identity compromise.
Effective response may require:
- global session revocation
- token invalidation
- mailbox rule review
- OAuth application audit
- device posture review
- sign-in log analysis
- consent and persistence investigation
Identity incidents are not isolated events. They are distributed trust failures across time, devices, sessions, and services.
The Strategic Reality
MFA is not broken.
The problem is that many organizations treat MFA as the end of the identity conversation when it is only one control inside a much larger trust system.
That is the real failure:
an incomplete identity model disguised as a mature security posture
The Hard Truth in One Sentence
Conventional MFA protects an important moment in the authentication flow. It does not, by itself, secure every route to account or session compromise.
Modern attackers increasingly target:
- the user during the flow
- the session after the flow
- the trust model around the flow
That is why checkbox MFA is not enough.
What This Means for Security Leaders
If your message is still:
“We enabled MFA, so we are covered”
your security model is incomplete.
If your strategy is:
- phishing-resistant authentication
- session governance
- device trust
- continuous reevaluation
- post-authentication detection
- hard recovery architecture
then you are defending identity at the level where modern attacks actually happen.
That is the difference between compliance language and operational reality.
Move Beyond Checkbox MFA
Understanding why MFA doesn’t stop phishing is critical for modern identity security.
Modern phishing does not stop at the login page. Your defenses should not stop there either.
For the wider attack chain, read How Cyber Attacks Happen. For the social-engineering path that leads into this topic, read Phishing Attack Explained.
If you want a serious view of your exposure, the right question is not “Do we have MFA?”
The right question is:
Can an attacker still obtain, replay, or persist a trusted identity state in our environment?
That is where real identity security starts.
Explore Security Services by DD Digital
MFA is one part of a broader security strategy. DD Digital focuses on practical WordPress security, including access controls, authentication, configuration, backups and recovery readiness.